Secure in Operation
Six cyber tools in one, at a lower total cost. Built for wind, solar and storage plant security — not just another generic enterprise security stack.
Security operations are normally bought as a shelf of separate products, each one licensed, integrated and staffed on its own. We roll the six capabilities a renewable site actually needs into a single pane of glass, every function reading from one model of the plant.
Stream modules
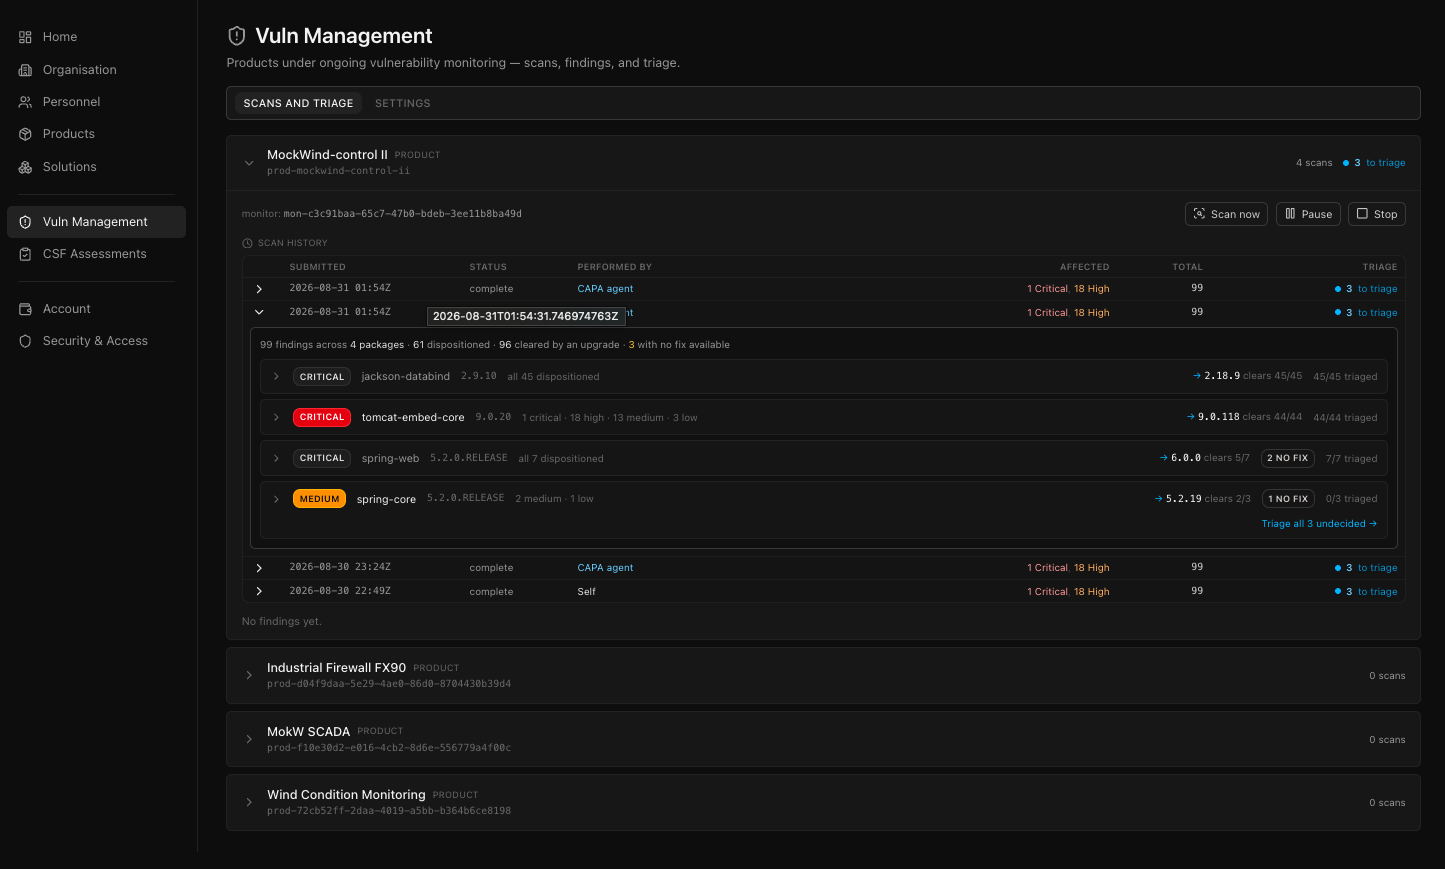
Vuln Management
Vulnerability intelligence triaged against the products and versions you actually run.
- PSIRT and CVE feeds monitored across the vendor ecosystem
- Triaged against the products and versions actually deployed
- Prioritised by exploitability and exposure
- Tracked to closure against an SLA
- Scan history and dispositioning per product
- add feature
Personnel Access
Who is on the plant, and what they are entitled to reach.
- Access control across staff, contractors and vendors
- Allow / deny / grey listing for IPs, PKI certificates and devices
- Standing remote-access monitoring under long-term service agreements
- Correlation and reconciliation against vendor access logs
- add feature
Intrusion Detection
Protocol-aware monitoring and anomaly alerting for renewables OT and DER.
- Anomaly alerting across CSIP, OCPP, Modbus and IEC 61968
- Passive monitoring of OT protocols for unexpected commands or config changes
- A learned baseline of normal operational behaviour per site
- Alerts on topology change and rogue devices
- add feature
Incident Response
Rapid, safe response when an intrusion is found.
- Rapid facility profiling to understand what is safe to touch
- Incident response playbooks tailored to OT constraints
- Desktop exercises and tabletop preparation
- Assurance that response tooling itself can be trusted
- add feature
Threat Intelligence
Real-time intelligence tied to the specific estate you operate.
- Real-time OSINT and proprietary threat feeds
- Malicious IP sources, product CVEs and organisational risk
- APT tracking with energy-sector profiles
- Dark web monitoring for exploits and exfiltration
- add feature
Change Control
Every software and configuration change tracked against a baseline.
- Software and configuration change tracked against a baseline
- Drift detection and alerting
- Change approval workflows, with two-person control for safety-critical changes
- An audit trail of who changed what, and when
- add feature
Cheaper
Six platforms, integrations and tools collapsed into one.
Focused
Built for energy and renewables IT and OT, not a generic enterprise SOC.
Integrated
Shares the plant model from the Site Journal, one source of truth.
Turnkey
Delivered ready to run, in-house or as a managed CAPA service.
Supports asset fleets from the outset
Australia leads the world in DER uptake, and is exposed to the threat vectors that come with it. After the attack on Poland’s grid, threats to DER infrastructure as a route to disable grid infrastructure have been telegraphed globally, and we must now defend against these threats.
CAPA has products that are adapted to manage the unique cyber landscape of distributed fleets, and the rapidly growing nexus between IT and OT.