Risk & Compliance
Escaping from spreadsheet mayhem. Meeting enhanced CIRMP and Tranche 2 SOCI obligations without a consulting engagement every cycle.
Compliance for a single generation site is not one framework. It is hundreds of controls from different legal sources, across every product and vendor on the plant, re-checked and re-evidenced every reporting period.
Using preloaded framework controls from SOCI and AES-CSF, CAPA removes the slog of mapping controls to evidence and resolving the overlaps between frameworks.
Clear obligations
Precise obligations flowed down to your major suppliers — not the kitchen sink.
Consequence-driven priorities
A small set of High Consequence Events, the crown jewels behind each, and mitigations that break the attack path.
Automate the grind
One body of work satisfies obligations across jurisdictions at once, produced from the live record on demand.
Stream modules
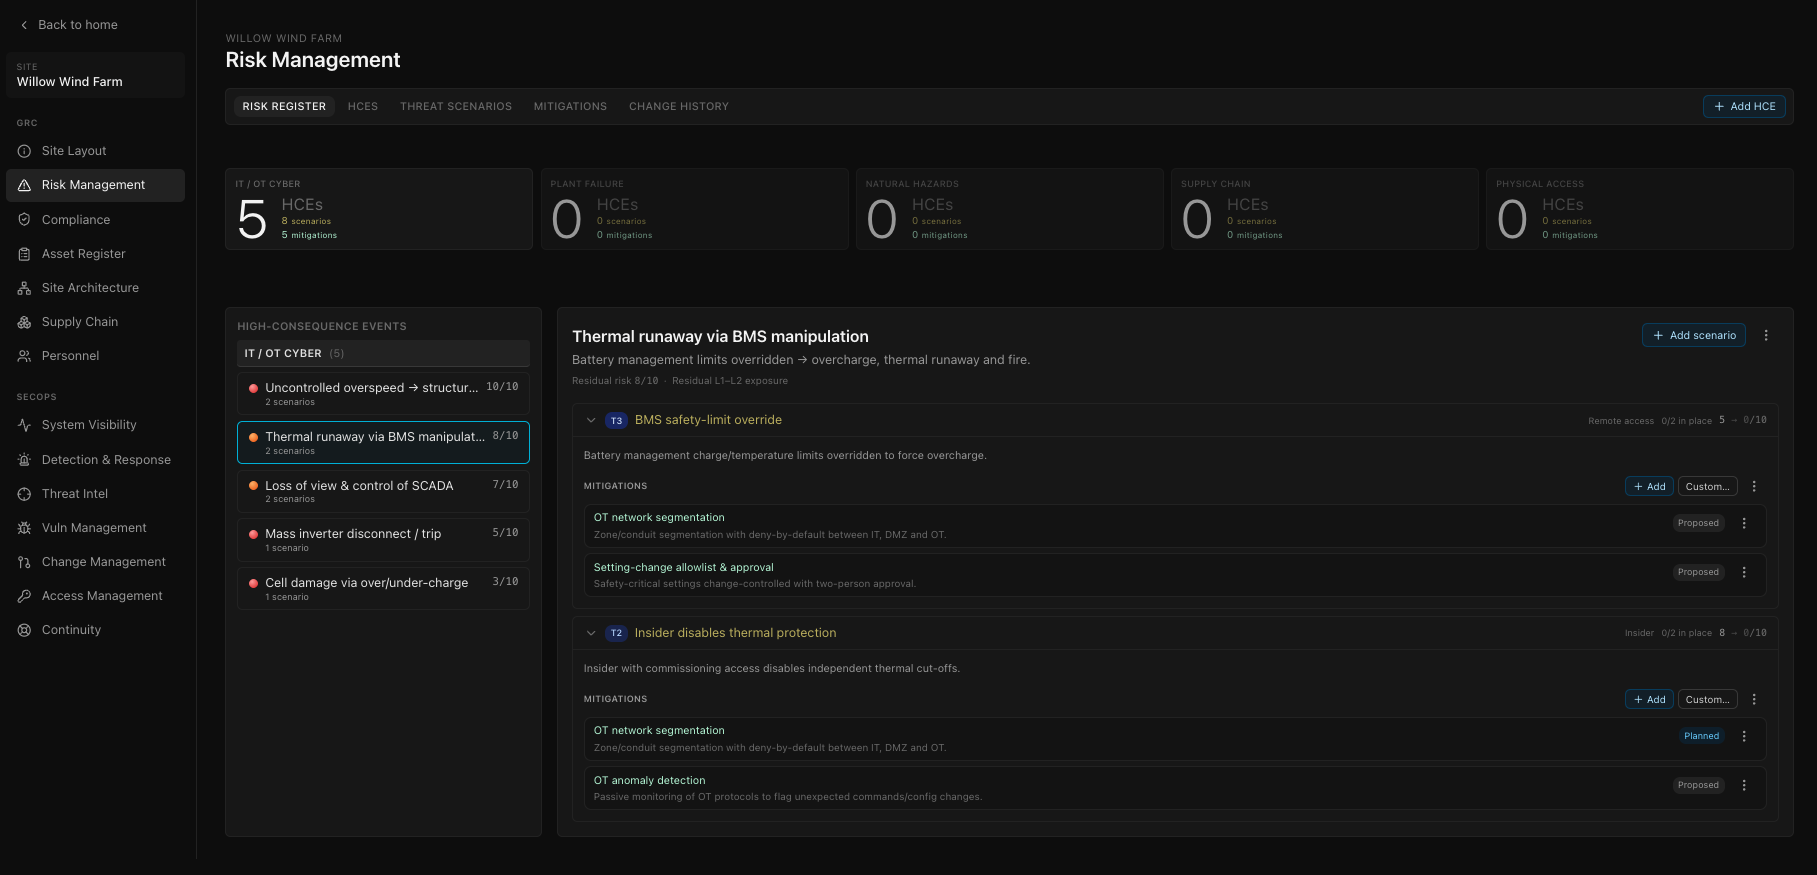
Risk Management
Consequence-driven risk built on a defined set of High Consequence Events.
- High Consequence Events (HCEs) defined per site
- The critical assets — the crown jewels — behind each HCE
- Threat scenarios mapped to each HCE, with kill-chains
- Mitigations that break the attack path, with residual-risk scoring
- Risk weighted by business-process impact (availability, control, data)
- Out-of-the-box risk models for renewables projects
- Audit and change history for CIRMP reporting
- add feature
Compliance
Framework controls mapped to evidence, with the overlaps between frameworks resolved once.
- Preloaded SOCI and AES-CSF control frameworks
- Support for custom corporate control frameworks
- Automated mapping of controls to evidence documents and certificates
- Overlaps between frameworks resolved once, not per framework
- Assessment scoring against control frameworks
- A documentation store for all compliance information
- Returns produced from the live record, on demand, in-house
- add feature
Supply Chain
Vendor and supply-chain assurance across the estate, including foreign interference risk.
- Supply chain mapping and analysis across the vendor base
- Foreign ownership, control or influence (FOCI) risk assessment
- Organisation- and product-level vendor assessment and audit
- SBOM ingestion and validation, where available
- Vendor-of-concern evaluation
- Outage and dependency analysis for critical vendors
- add feature
Supply chain catalogs
Understanding all aspects of your supply chain - mapping the software and hardware, understanding the risks such as FOCI, and assigning clear compliance obligations on your vendors is complex.
CAPA has developed comprehensive vendor product catalogs that allows you see the compliance status of vendors and their products, and to leverage assessments already made in other similar deployments.
Ditch the spreadsheets. Cut compliance overhead by ~50%.